The Basics of Decentralized Identity (DID) and Self-Sovereign Identity (SSI)
The Basics of Decentralized Identity (DID) and Self-Sovereign Identity (SSI)
A practical guide to understanding decentralized identity (DID), self-sovereign identity (SSI), and Web3 and blockchain-based identity.
By Memdeklaro | May 15, 2026
Introduction
Decentralized identity (DID) is an emerging technology designed to give people greater control over their personal data, including the ability to choose what information they disclose and to whom.
As part of the broader fields of digital identity, self-sovereign identity and Web3 identity, decentralized identity focuses on secure and privacy-respecting ways to store, manage and verify digital credentials and attestations.
Decentralized identity represents a shift away from centralized databases, information silos and single points of failure. Many DID implementations aim to provide robust, interoperable and universally applicable systems that can be used across fields such as education, employment, healthcare and finance.
The Basics: Public Key Cryptography
Public key cryptography is the foundation of many DID and SSI implementations. It is commonly used in digital wallet software.
In public key cryptography, a user generates a large random number that serves as their private key. From this, a corresponding public key is derived. The private key must remain secret like a password, while the public key can be shared with others like a username.
Once a key pair has been generated, the user can start to sign and encrypt messages. Digital signatures provide verifiable evidence of authorship or provenance, while encryption helps protect privacy. The private key is used to generate signatures and decrypt messages, while the public key is used to verify signatures and encrypt messages.
The same technology finds use in encrypted messaging applications, federated social networks and cryptocurrency wallets, where it is often associated with Web3 identity or blockchain identity.
The Use Case: Decentralized Credentials and Logins
Once users have generated their cryptographic key pairs, they can associate credentials and attestations to their public keys and store these in their digital wallets. Data might include a username, date of birth, university degree or membership in an organization. Users can choose which information to associate with their identity, and some implementations also support pseudonymity.
Some DID frameworks use a blockchain to maintain a tamper-resistant public record. Others store attestations privately on the user's device, use decentralized storage systems such as IPFS, or rely on web APIs.
Some implementations also incorporate zero-knowledge proofs, which can improve privacy by allowing a claim to be verified without disclosing the underlying personal information. For example, someone could prove that they are over 18 without revealing their exact date of birth or sharing a photograph.
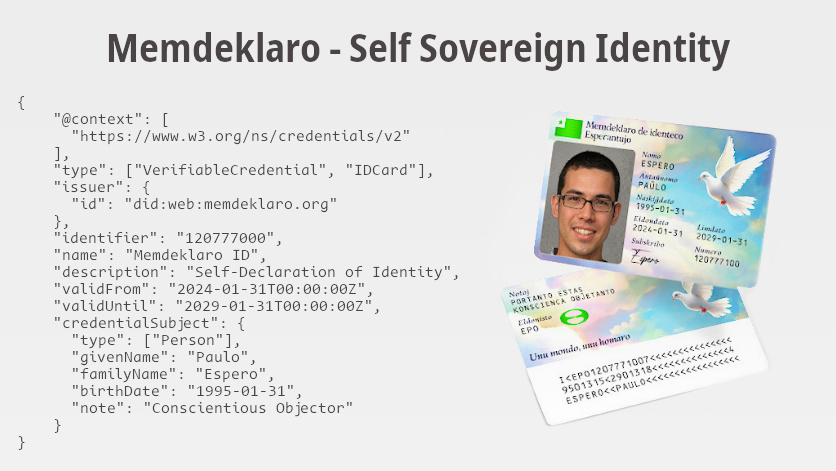
Credentials can be issued and digitally signed by a trusted authority, such as a university issuing a diploma or an employer issuing an employee badge as a verifiable credential. Alternatively, individuals can create and sign their own attestations, such as a name or bio, as a self-issued or self-attested credential. The Memdeklaro self-declaration of identity is an example of a self-attested credential.
A credential's digital signature can be verified using the issuer's public key, helping establish its authenticity without relying on paper documents, telephone calls or proprietary APIs.
Physical documents, including diplomas, membership cards and NFC badges, remain valid and widely used. Decentralized identity simply offers an additional option that can reduce paperwork, save time and, when combined with zero-knowledge proofs, improve privacy.
DID protocols can also enable users to login to services without a separate username and password. Examples include using a Web3 wallet to send and receive cryptocurrency, an employer-issued certificate to access a company network, or a digital identity wallet to access health records or schedule an appointment.
Instead of entering a password, the user generates a signature using their private key. The service then verifies the submitted signature using the user's public key. This approach can improve security because the private key remains on the user's device and is not shared with third parties.
A Danger: Monopolies on Credential Issuance
However, decentralized identity can still be vulnerable to centralized control, particularly when a single authority controls the issuance of verifiable credentials.
For university degrees, employment records or organizational memberships, this is generally less problematic because multiple competing issuers exist. People can choose among a variety of educational institutions, employers, clubs and associations.
The primary concern is a monopoly over the foundational layer of identity: the name, photograph and date of birth to which other credentials are linked.
If a DID implementation requires government-issued documents, such as a passport, birth certificate or national identity card, as a mandatory foundation, it perpetuates the same exclusionary practices found in traditional identity systems.
In the legacy system, a person's foundational identity is usually established when their parents register their birth and the state issues a birth certificate. As an adult, that person uses the birth certificate to obtain a national identity card or passport, which can then be used to apply for employment, open a bank account or rent an apartment.
However, this process creates a single point of failure with potentially devastating consequences. Parents may be unable or unwilling to register a child's birth, or the country where the child is born may refuse registration under certain circumstances, such as when the parents are undocumented or unmarried. In such cases, no foundational identity document may be issued.
As an adult, the individual may have no way to register their birth independently of their parents, religion or state bureaucracy. Without a foundational document, they may face exclusion from ordinary social and economic participation, without appeals or alternatives.
Similarly, people fleeing abuse, violence or war may lose access to their birth certificates or passports and be unable to obtain replacements.
Lack of government ID currently excludes millions of people worldwide from employment, housing, healthcare, banking, contracts and other everyday necessities.
If DID implementations treat government documentation as the only trusted means of verifying a person's name or date of birth, the decentralization is lost and the same forms of exclusion persist.
Memdeklaro: A Solid Foundation for Self-Sovereign Identity
Memdeklaro takes a different approach by allowing people to establish their own foundational identity through self-declaration.
With Memdeklaro, users can self-declare their own name, date of birth and personal ties independently of their birth parents or country of birth, without requiring government-issued identification. After the user generates their Memdeklaro self-declaration, they can independently associate it with other credentials, such as education, work experience, memberships, finances and references.
Example Self-Asserted Credential
{
    "@context": [
      "https://www.w3.org/ns/credentials/v2"
    ],
    "type": ["VerifiableCredential", "IDCard"],
    "issuer": {
      "id": "did:example:paulo-espero"
    },
    "identifier": "1207771000",
    "name": "Memdeklaro Self-Declaration of Identity",
    "description": "Generated at https://memdeklaro.org",
    "validFrom": "2024-01-31T00:00:00Z",
    "validUntil": "2029-01-31T00:00:00Z",
    "credentialSubject": {
      "id": "did:example:paulo-espero",
      "type": ["Person"],
      "givenName": "Paulo",
      "familyName": "Espero",
      "birthDate": "1995-01-31",
      "note": "Conscientious Objector"
    }
}
Memdeklaro self-asserted credentials aim to give everyone an accessible foundation on which to build their lives. The broader vision is a world in which personal beliefs and individual efforts matter more than arbitrary circumstances of birth.
Note: Memdeklaro does not implement a blockchain or act as a trusted authority. Instead, users use the public domain template to generate and assert their own declarations of identity, reflecting the project's philosophy of freedom of identity.
Anyone wishing to use a Memdeklaro declaration with a Web3 wallet or DID framework must sign it with their own private key as a self-signed credential.
Furthermore, the Memdeklaro web application is designed solely for self-declaration of personal identity. It does not manage or verify third-party credentials relating to education, employment, finance, contracts or references. However, users may independently use a Memdeklaro self-declaration as a foundational identity layer to build their reputation on third party platforms, frameworks and communities.
Conclusion
Decentralized identity, also known as self-sovereign identity, can help people manage their credentials more efficiently, streamline authentication through cryptographic signatures, and improve privacy through techniques such as zero-knowledge proofs.
However, these benefits are lost if trusted authorities have a monopoly over foundational identity, particularly when government-issued identification is the only accepted way to verify a person's name or date of birth.
Self-declarations such as Memdeklaro can help prevent people from being locked out by providing an accessible foundation for identity. Verifiable credentials can then be used to establish claims about education, employment, memberships, and other aspects of a person's life.
As the technology develops, DID and SSI may become increasingly useful tools for managing accounts and credentials, reducing information silos and improving privacy.
Tags: decentralized identity, self-sovereign identity, web3 identity, self-attested verifiable credentials, self-issued verifiable credentials, self-attestation
See also: Guide to Non-Government ID: Memdeklaro vs. Digitalcourage vs. World Passport